“We’re moving into a world where adversaries automate everything in the kill chain that doesn’t require deep creativity,” former CISA Director Jen Easterly warned in response to a November 2025 misuse report from frontier AI company Anthropic.
In November, Anthropic disclosed it had disrupted a cyber attack and data extraction operation that targeted dozens of major companies and government agencies. The perpetrators (allegedly part of a Chinese state-sponsored group) were using Anthropic’s Claude Code to achieve an unprecedented level of cyberattack automation, using only occasional human guidance at critical moments.
For large enterprises with robust cybersecurity teams, this is concerning. For small businesses and non-governmental organizations (NGOs) which lack those resources, this is terrifying.
AI Makes Phishing Faster, Cheaper, and More Effective
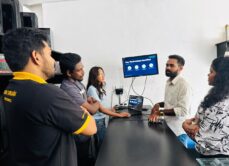
Organizations are already struggling with AI’s impacts on phishing and social engineering. At the “Changemakers Day” the day before the October Mastercard Inclusive Growth Summit in Kuala Lumpur, Brian Cute, Interim CEO of GCA, demonstrated what AI-enabled phishing looks like. He showed AI drafting polished spear-phishing messages in real time, with words streaming onto the screen far faster than a human could type.
As one attendee put it afterward, “It’s less ‘shame on the victim’ now, because it’s less reasonable to expect someone to see through it.”
The presentation used one of many demos produced by CivAI, a nonprofit dedicated to helping people internalize the impacts of AI on society. CivAI’s non-public demos lay out vivid AI misuse scenarios, including personalized phishing emails; image, audio, and video deepfakes; disinformation; election interference; and biological threats. NGOs and individuals can request access or view CivAI’s publicly-accessible demos online.
A recent study found that AI-personalized phishing emails achieved more than 4x the clickthrough rate of traditional mass phishing (54% vs. 12%). The conventional advice to watch for typos, broken English, and sloppy formatting is insufficient.
AI Exposes New Attack Vectors
Other AI technologies have been contributing to growth in new attack vectors as well. In 2024, scammers used AI deepfakes to pose as executives on a video call and defraud a multinational firm out of $25 million. North Korean operatives have used AI to secure and maintain thousands of roles at Fortune 500 companies to extract value and sensitive data. The FBI recently warned about deepfaked audio and video being used in kidnapping scams.
Beyond phishing and social engineering, AI is autonomously finding and exploiting technical vulnerabilities. The operation described in Anthropic’s November 2025 report had AI handling 80-90% of tactical operations independently — not just drafting convincing emails, but conducting reconnaissance, developing exploits, harvesting credentials, and assessing stolen data at superhuman speeds.
Tactics Spread Quickly in the Underground Economy
What state actors are doing today, organized crime will be doing tomorrow. According to the United Nations Office on Drugs and Crime (UNODC), the sprawling complexes that house industrial scale fraud operations across Southeast Asia can sometimes approach the scale of small cities, and are estimated to generate a combined $40 billion annually. These massive criminal enterprises are integrating AI into their operations at an accelerating pace, with many already using AI for translation and automated outreach. According to a recent report from KnowBe4, 82.6% of phishing emails detected between September 2024 and February 2025 were drafted using AI.
Law enforcement experts expect the majority of the market to have fully integrated agentic AI within two years. We are living through the last moments of the era where obscurity and small scale can offer adequate protection.
Smaller Organizations Are Uniquely At Risk
Municipalities, NGOs, and Small and Medium Enterprises (SMEs) — organizations frequently without dedicated security teams — will increasingly face attacks at the same level of sophistication and personalization as those currently aimed at Fortune 1000 companies.
AI has simultaneously reduced the costs of committing cybercrime at scale and increased the profits by helping attackers monetize the information they steal. Previously, a criminal investing hours in a personalized attack needed a high-value payoff. Now most of that personalization can be automated for pennies. Campaigns against hundreds of small organizations could become more profitable than concentrated attacks on hardened enterprises.
SMEs also frequently lack the ability to absorb the losses associated with a breach. Large enterprises can afford to pay out millions to resolve the fallout of cyberattacks, but small groups like school districts, medical practices, and faith-based organizations with donor databases could find themselves scuttled by a ransom or even legal fees alone. According to a 2024 survey, 60% of small businesses view cyberattacks as their biggest threat.
The asymmetry between attacker capability and defender resilience is most severe for small organizations. It’s critical to secure cyber infrastructure now, before they become victims of cybercriminals.
Securing Small Organizations Against AI-Enabled Cybercrime
Cute’s presentation at the October Summit also highlighted how AI can be harnessed for good, not just mischief. By using AI to scale cyber capacity building, GCA is introducing hands-on guides, self-paced courses, and collaborative programs with partners to expand cybersecurity skills globally. In the face of this AI-driven cybercrime wave, these efforts aim to strengthen the knowledge and capabilities of individuals and organizations alike, helping build a more secure and resilient digital ecosystem for everyone.
A global, coordinated, and comprehensive response to these new kinds of threats requires both collective action across many defenders and individual action on the part of vulnerable organizations — neither can suffice on its own.
Governments, technology companies, and civil society must work together to invest in technological safeguards, infrastructure-level defenses, cross-border threat monitoring, and societal preparedness.
In the meantime, organizations and individuals can’t afford to wait for collective action. Preparing for the cyber threats posed by AI requires a renewed commitment to uplifting organizational security standards, including strong passwords, multifactor authentication, phishing awareness, least privilege principles, input sanitization, robust backups, patch automation, and rate limiting endpoints.
GCA works at two distinct levels to make the Internet and its users safer. GCA is using AI to automate and scale cybersecurity protection, enabling more people to protect themselves, faster, while simultaneously strengthening the technical infrastructure of the Internet by identifying and disrupting malicious traffic, abusive domains, and routing incidents that enable cybercrime. GCA also works in partnership with governments, industry, and civil society organizations to create communities of action that can respond to these threats at scale.
The wave of AI cybercrime is already rolling towards the shore. Organizations don’t have long to prepare before it hits.